Since 2006, Sasha Justmann has been driving the digitalisation of the insurance industry — as a founder, CTO, advisor, thought leader and winner of more than 20 innovation awards for digital standards, processes, interfaces and platform economics.
ABOUT ME
SASHA JUSTMANN
"ON THE WINNERS' PODIUM AS AN INNOVATION LEADER WITHOUT INTERRUPTION SINCE 2006."
20 YEARS OF TOP RANKINGS FOR DIGITAL PROCESS QUALITY
Since 2006, Sasha Justmann has been supporting the insurance industry in digitalising its processes. As both an insurance broker and an IT service provider, he understands the needs of brokers just as well as the technical possibilities of modern IT. He has made it his mission to enable advisors, sales organisations, platforms and insurance companies to make the leap into a digitally connected future.
He is the founder of zeitsprung GmbH, which he developed from 2009 to 2026 as managing partner into the market and innovation leader for interface automation.
As Chief Technology Officer of the blau direkt group, he was responsible for software development, IT product management, infrastructure and IT compliance — followed by a move to the advisory board.
As deputy spokesperson of the technical standardisation committee of BiPRO e.V., he has been successfully accompanying the association's standardisation projects for more than 10 years, shaping the entire industry with his expertise and foresight.
Expertise
CORE COMPETENCIES
Modern IT & software development
M&A transaction leadership
Entrepreneurship & scaling
IT security & certification
Product & innovation management
Compliance & risk management
Process automation & interfaces
Industry standardisation (BiPRO)
Career
PROFESSIONAL MILESTONES
Current
Advisory Board Member
blau direkt Gruppe
Lübeck
since 2026
5 months
Strategic sparring partner for the management, subsidiaries and sister companies as well as the shareholders in the further development of the digital infrastructure and technology platform.
Technological leadership of the entire group: software development, IT product management, infrastructure and IT compliance.
IT strategyPlatform architectureIT complianceLeadershipProduct management
Founder & Managing Partner
zeitsprung GmbH
Pforzheim
2009 — 2026
17 years 10 months
Built and scaled the IT service provider into the market and innovation leader for interface automation in the insurance industry. Led the sale of the company to an investor.
A selection of the most important industry and innovation awards from more than a decade.
BiPRO Award
2017, 2018, 2019, 2022 — 1st place (including the "Consumer Non-TAA" category), 2024 — 2nd place service provider, 2026 — 1st place consumer for blau direkt.
since 2017
Innovator of the Year
brand eins & Statista: top rankings in "Technology & Telecommunications" as well as for corporate culture.
2017 · 2018 · 2019 · 2021
German Innovation Award
Winner — "Excellence in Business to Business, Industry Specific and Service Softwares" for the automated document service.
2020 · 2022
German Brand Award
"Excellence in Brand Strategy, Management and Creation" as well as "Business Model & Product Innovation".
2018
YouGov Customer Innovation
Cross-industry award for the development of the document service.
2016
kununu Top Company Award
One of the best IT employers, based on above-average employee ratings.
2022 · 2025
Facts & figures
ACHIEVEMENTS
6 achievements1 exit17 years
A selection of the most important milestones in company management, M&A and innovation.
18 years of top-level leadership
Commercial and technological leadership of zeitsprung GmbH from 2009 to 2026.
2009—2026
8 years on the winners' podium
Consistently 1st or 2nd place at the BiPRO Award since 2017 for excellent digital processes and interface quality.
1st / 2nd place
4× "Innovator of the Year"
Listed by brand eins and Statista as one of Germany's most innovative technology companies.
2017—2021
Successful exit
Designed and led the M&A transaction for the strategic sale of his own company to an investor.
M&A
Scaling at C-level
Appointed CTO of the blau direkt group to steer the group-wide IT, followed by an advisory board role.
CTO
First-class track record
Officially certified top marks ("fullest recognition in every respect") for quality of work, problem-solving skills and leadership from colleagues, clients, partners and suppliers.
Grade 1
TALKS & PUBLICATIONS
SPEAKING
29 contributions15 locations6 years · 5 formats
Due to the large number of publications, only excerpts from the last 2 years are shown here.
2026
KI trifft Versicherungsprozesse: Chancen, Grenzen und neue Standards
Panel · Neuss
2026
Impuls zur Lage der Versicherungswirtschaft
Talk · Karlsruhe
2026
Wie Maklerbetriebe wachsen und KI-first-Ansatz
Podcast · Pfefferminzia
2026
Ohne saubere Datenbasis keine KI
Article · Finanzwelt
2026
KI übernimmt das Büro: „Weniger Maklerbüro und viel mehr Makler werden"
Panel · Helsinki
2025
Technologie mit Weitblick: Sasha Justmann prägt die IT-Strategie bei blau direkt
Interview · Finanzwelt
2025
If ist not a hell yeah its a f**k no!
Interview · Provision
2025
Insights on tour Maklervertrieb: Ein Blick in die Zukunft mit Sasha Justmann
Podcast · Neuss
2025
KI im Makleralltag
Interview · Lübeck
2025
Versicherungs-IT heute und morgen
Talk · Karlsruhe
2025
Kritische Fragen treffen auf klare Aussagen
Panel · Krakau
2025
Tech-Visionär Sasha Justmann übernimmt technologische Führung der blau direkt-Gruppe
Interview · Lübeck
Year
Title
TYPE
Location
2026
KI trifft Versicherungsprozesse: Chancen, Grenzen und neue Standards
Panel
Neuss
2026
Impuls zur Lage der Versicherungswirtschaft
Talk
Karlsruhe
2026
Wie Maklerbetriebe wachsen und KI-first-Ansatz
Podcast
Pfefferminzia
2026
Ohne saubere Datenbasis keine KI
Article
Finanzwelt
2026
KI übernimmt das Büro: „Weniger Maklerbüro und viel mehr Makler werden"
Panel
Helsinki
2025
Technologie mit Weitblick: Sasha Justmann prägt die IT-Strategie bei blau direkt
Interview
Finanzwelt
2025
If ist not a hell yeah its a f**k no!
Interview
Provision
2025
Insights on tour Maklervertrieb: Ein Blick in die Zukunft mit Sasha Justmann
Podcast
Neuss
2025
KI im Makleralltag
Interview
Lübeck
2025
Versicherungs-IT heute und morgen
Talk
Karlsruhe
2025
Kritische Fragen treffen auf klare Aussagen
Panel
Krakau
2025
Tech-Visionär Sasha Justmann übernimmt technologische Führung der blau direkt-Gruppe
Interview
Lübeck
Blog
INSIGHTS
Analysis, context and hands-on articles on standards, regulation and technology in the German insurance IT market.
{
"content": "25.09.2026 Sasha Justmann\n Green APIs: Why Sustainability in Insurance IT Begins with Data\nWhy sustainability in insurance IT does not start with reporting, but with the question of how data is structured.\n\nSustainability is long past being a peripheral issue in the insurance industry, affecting only asset management or product development. Two questions are frequently conflated here: How can IT make its own operations more sustainable – and how can IT help to make sustainability measurable in the rest of the value chain? Both perspectives directly affect the BiPRO ecosystem.\n\n Regulatory Pressure: Why 2026 is Becoming a Turning Point\n\nFor many insurers, the driver is regulation. Although the EU Commission’s Omnibus I package has raised the CSRD thresholds – generally, only companies with more than 1,000 employees and over 450 million euros in turnover will be mandated in future, 2026 is considered a transitional year for CSRD, ESRS revision, and the EU Taxonomy. At the same time, starting in 2026, small and non-complex credit institutions as well as captive insurance undertakings will also fall under the reporting obligation for the first time, including climate protection reporting according to ESRS E1, coupled with the EU Taxonomy Regulation regarding the disclosure of taxonomy-aligned revenues and investments.\n\nWhat looks like a financial reporting issue is actually a data problem: Without structured product, contract, and claims data, neither a corporate carbon footprint nor a taxonomy ratio can be reliably reported. This is precisely where the IT perspective begins.\n\n Sustainability in IT: Making the Infrastructure Itself Greener\n\nThe first perspective concerns IT as a driver of resource consumption. With the Energy Efficiency Act (EnEfG), the German legislator has imposed a dedicated energy law compliance regime on data centres for the first time: New data centres starting operations from 1 July 2026 must maintain a PUE (Power Usage Effectiveness) value of maximum 1.2, existing facilities must follow suit with 1.5 by 2027 and 1.3 by 2030. In addition, there is a phased obligation for waste heat utilisation and – already since 2024 – the requirement to increasingly cover energy demand from renewable sources, fully accounted for by balance sheet from 2027. Violations risk fines of up to 100,000 euros, and in certain cases up to 200,000 euros. Anyone purchasing IT services or operating their own data centres should be aware of these figures – not only for compliance reasons, but because they are increasingly becoming part of tender criteria.\n\nBeyond hardware and hosting, however, it is worth looking at a dimension that is often overlooked in the discussion: data architecture itself. Every unstructured interface – a PDF that first needs to be read via OCR, a portal that is scraped, a document that an AI must first \"understand\" before the contained data can be further processed – generates additional computing effort that simply does not arise with a standardised, structured interface. A BiPRO-normalised message is already available in machine-readable form and does not need to be reinterpreted. Viewed as a single transaction, this difference is small – but across a market-wide BiPRO infrastructure connecting a multitude of insurers with thousands of distribution partners, the effect scales: a transformation normalised once is reused many times over, instead of every connection operating its own individual data preparation. Whether and to what extent this translates quantitatively into CO₂ equivalents has not yet been systematically investigated – but the connection between the degree of standardisation and avoided processing effort is obvious and would be worth proving empirically.\n\n Sustainability Through IT: When Data Makes Risks Visible\n\nThe second perspective reverses the relationship: IT not as a consumer, but as an enabler of sustainability. And here, claims statistics provide a drastic background. Natural disasters caused global damages of around 224 billion US dollars in 2025, of which approximately 108 billion US dollars were borne by the insurance industry – around 17,200 people lost their lives, significantly more than in the previous year. Over 90 percent of these damages are attributable to weather events, not earthquakes or other geological causes. The European Environment Agency reaches a similarly urgent conclusion in its first European Climate Risk Assessment: 36 identified climate risks across five risk clusters, more than half of which already require urgent action today.\n\nFor insurers, these figures are not abstract sustainability metrics, but their core business – premium calculation, reinsurance strategy, location assessment. However, for climate risk data, property, and natural hazard claims data to be factored into tariffing and claims processes in the first place, they must be structured and interface-compatible. How practically this is already being implemented was demonstrated at the Sustainable Insurance Convention 2026 in Leipzig: A practical example presented there by an insurer has been trialling a \"green cycle\" in the motor insurance line for six months, where repair shops can source used replacement parts for accident vehicles via specialised platforms – a concrete circular economy approach in claims management that would not be scalable without a structured connection to these platforms. Also noteworthy is a second example from the same event: participating companies presented the concept of a central \"trust platform\" that bundles ESG-relevant corporate data modelled on credit bureaus – instead of every insurer having to collect the exact same data individually and manually from its existing customers. This very principle – one source, many users, instead of many individual queries – is essentially the same one that BiPRO interfaces have been implementing for contract and claims data for years.\n\n Action Areas: A Checklist for Self-Assessment\n\nIf you want to check in your own company or with partners in a structured manner where sustainability and IT converge, you can use the following questions as a guide:\n\n- Data Centre & Hosting: Do your own or procured data centres already meet the EnEfG requirements regarding PUE value, share of green electricity, and waste heat utilisation – and is this contractually fixed with service providers?\n- Data Architecture: How often is the same information (contract data, documents, portfolio data) redundantly collected anew, rendered, or extracted via AI from unstructured sources, even though a structured interface already exists or would be possible?\n- Supply Chain & Service Providers: Can IT service providers and software houses provide evidence of energy efficiency and sustainability measures upon request, for example within the scope of supply chain due diligence obligations?\n- Product Level: Is it recognisable within your own product portfolio which sustainability aspects a tariff addresses – climate protection, circular economy incentives, social components – or does this information exist only scattered across marketing texts?\n- Reporting Capability: Can ESG-relevant data be exported in machine-readable form from core systems, or would they have to be compiled manually for every CSRD or taxonomy disclosure?\n\nParticularly the last and second-to-last points show where there is a gap in the industry's current data model.\n\n Impulses from the Industry Association: BiPRO e.V. Explores Action Areas\n\nThat sustainability is also becoming relevant for standardisation work itself is currently evident at BiPRO e.V. As part of ongoing digitalisation offensives and standardisation projects, the association is currently looking into which action areas in this field could become relevant for its members. Discussions include reducing the environmental footprint of the member companies themselves, the question of whether the use of BiPRO standards in itself constitutes an independent sustainability contribution – a thought that coincides with the consideration outlined above regarding avoided redundant data processing – as well as concrete use cases: How could normalised interfaces and recommendations based on them also support the product decisions of customers in the future, for example by making sustainability features of insurance products comparable? Naturally, a finished result is not yet available here – the exploration is in an early phase. Nevertheless, it is noteworthy because it shows that the topic has arrived in the industry's standardisation work and is no longer discussed solely within individual companies.\n\n Looking Ahead: A Sustainability Attribute in the BiPRO Product Model\n\nOne of the use cases outlined above – supporting product decisions through normalised interfaces – is already taking concrete shape. The product model of the BiPRO standards world – described essentially by the 300ff. standards and particularly Standard 310 – already maps today what components an insurance product is composed of and how this structure is specified line-by-line via the TAA standards (421 to 426). What was previously missing in this model was a standardised, transferable way to map sustainability aspects of a product – not as free text in the policy conditions, but as a structured attribute that an insurer maintains once and which automatically reaches all connected distribution partners via existing interfaces – in comparative calculators, broker management programs, and customer advisory systems. Exactly this gap is what current standardisation work is addressing: In the ongoing release generation, a corresponding attribute is currently being developed, which is scheduled to be ready for concrete use with future releases.\n\nSuch an attribute does not have to be binary (\"sustainable yes/no\"), but can map multiple dimensions, similar to the logic of the ESRS environmental standards: Does the product contain incentives for the circular economy? Do climate risk data factor into tariffing? Is there a social component? Given the growing number of market monitors and product databases for sustainable insurance products, which are currently emerging in parallel and inconsistently, a unified database via established BiPRO interfaces is the more obvious path than every provider defining their own format.\n\n Conclusion\n\nThe sustainability debate in insurance IT is often conducted either as a pure compliance topic or as a pure infrastructure topic. Both fall short. The actual lever lies where both perspectives converge: in data that is captured in a structured manner once, but can be used multiple times – for the automotive repair shop just as much as for the sustainability report. Standardisation was never an end in itself for the insurance industry. When it comes to sustainability, it becomes a prerequisite."
}
{
"content": "14.09.2026 Sasha Justmann\n Scaling Without Loss of Control: How Compliance Processes Grow with Expanding InsurTechs\nAn article on entrepreneurship, scaling, and compliance in German insurance IT\n\n When Growth Outpaces the Organisation Itself\n\nThe German InsurTech landscape, long characterised by established, slowly growing structures, is undergoing a profound transformation: digital technologies and artificial intelligence are fundamentally changing business processes, products, and customer experiences, unlocking new potential for growth and efficiency. For founders in this environment, however, an uncomfortable question arises early on: how can rapid growth be reconciled with the strict regulatory requirements of a heavily regulated industry without compliance either becoming a brake on growth or—worse still—a neglected side issue?\n\nA PwC study among compliance officers at German FinTechs and InsurTechs (Source: PwC) gets straight to the heart of the core problem: rapid growth, resource bottlenecks, and young employees who predominantly do not come from the financial sector mean there is substantial room for improvement in compliance matters. It is precisely this tension—between growth pressure and regulatory maturity—that shapes the day-to-day business reality of many insurance startups.\n\n Compliance Is Not an Optional Extra, But a Prerequisite for Growth\n\nIt is remarkable how strongly the topic is already anchored at the executive level in practice: in almost every second company surveyed by PwC, responsibility for compliance lies directly with the founder or management—not with a subordinate specialist department. This is also an expression of regulatory reality: 82 percent of the compliance officers surveyed state that they deal with the topic primarily out of regulatory obligation, while around half additionally cite requirements from customers or investors as drivers.\n\nThis distribution shows that compliance in growing InsurTechs is increasingly understood as a prerequisite for growth rather than a completed project. The actual bottleneck lies less in a lack of awareness of the problem than in practical implementation: managing compliance overhead in day-to-day business is considered the biggest challenge during the growth phase.\n\n Why Scaling Poses Specific Challenges for Compliance Processes\n\nFor insurance startups, several factors intensify simultaneously as the business scales:\n\n- Regulatory breadth increases. With a growing customer base, new product lines, or expansion into further European markets, the applicable regulatory requirements also grow—ranging from BaFin guidelines and the GDPR to sector-specific regulations such as DORA.\n- Staff structure changes faster than processes. Since many employees in rapidly growing InsurTechs do not come from the financial sector, they often lack the intuitive sense for regulatory pitfalls that has developed over years in established insurance companies.\n- Resource bottlenecks intensify with the pace of growth. Compliance teams designed for a specific company size quickly reach their capacity limits during rapid growth—often precisely during the phase when regulatory attention is most urgently needed.\n\n Viewing Regulation as a Framework and Competitive Advantage\n\nAn important shift in perspective for growing InsurTechs lies in understanding regulation not solely as a burden, but also as an opportunity for differentiation. Although the regulatory environment in Germany and the EU, shaped in particular by BaFin and the GDPR, imposes high demands, it simultaneously creates trust and offers the opportunity to develop data-compliant and secure solutions that are also perceived as a quality feature internationally. For an InsurTech looking to position itself against established insurers, a demonstrably robust compliance organisation can thus become a trust and sales argument in its own right—especially when dealing with larger, more conservative distribution partners or institutional customers. Companies consistently view this step themselves not as a one-time milestone, but as a continuously nurtured process with annual monitoring audits—an approach that sends a clear signal in a fast-growing market segment: management systems and robust compliance structures are not an afterthought, but part of a professional market presence.\n\n Methods for Regulatory Experimentation During Growth\n\nScaling without loss of control does not mean securing every innovation down to the last detail from a regulatory perspective in advance. In practice, several approaches have proven effective in combining freedom to innovate with regulatory certainty:\n\n- Early anchoring at the founding level. If compliance is anchored in corporate management from the outset rather than becoming a separate function as the company grows, regulatory requirements can be integrated into product decisions from the beginning instead of being retrofitted later.\n- Thinking about scalable compliance infrastructure from day one. Instead of optimising compliance processes for the current company size, it is worth looking at structures that remain viable even with a significantly larger business volume—for instance, through the early use of specialised RegTech solutions for standardised review and reporting processes.\n- Establishing onboarding and training as a continuous process. Since many new employees are from outside the industry, a basic regulatory understanding should not be anchored as a one-time induction, but as an ongoing component of the corporate culture.\n- Actively anticipating investor and customer requirements. Since investors and customers increasingly impose their own compliance expectations alongside pure regulation, looking beyond minimum legal requirements is worthwhile to avoid subsequent demands during funding rounds or partnerships.\n\n In Practice: Compliance Building Blocks for the Founding Phase\n\nThese principles remain abstract unless broken down into the concrete day-to-day reality of founding a company. Several directly actionable building blocks can be derived from practice that can be realised even without a large compliance department:\n\n- Clearly assign responsibility from day one. Instead of leaving compliance open \"until someone is in charge\", a person should be explicitly designated as the compliance officer within the founding team—usually management itself. This costs nothing, but prevents regulatory questions from getting lost in daily business because no one feels specifically responsible.\n- A living, one-page compliance document instead of a binder. A simple, continuously maintained document—such as \"Which regulations affect us, who checks what, how often?\"—is often sufficient in the early phase. What matters is not the completeness of a later compliance manual, but that the most important obligations are recorded in writing at all and updated regularly.\n- Add a compliance module to the onboarding checklist for new employees. Since many new employees are from outside the industry, a short, mandatory introductory point during onboarding helps—such as a half-hour explanation of the most important dos and don'ts in customer contact, data processing, and sales statements. This can be established as a fixed component of every induction with manageable effort.\n- Four-eyes principle for sales statements and advertising material. Particularly in sales, regulatory risks often arise not from malicious intent, but from thoughtless formulations in product descriptions, landing pages, or sales collateral—such as impermissible yield promises or unclear risk disclosures. A simple rule that new sales texts are proofread by a second person for regulatory pitfalls before publication can be implemented without additional staff.\n- Fixed, recurring compliance meetings instead of ad-hoc reactions. A short monthly or quarterly meeting to discuss open regulatory questions, new guidelines, and current review points prevents compliance from only becoming a topic when a concrete problem has already occurred.\n- Using investor and partner inquiries as an early warning system. Compliance-related questions from funding rounds or distribution partners should be systematically collected and answered rather than treated as a one-time hurdle. Recurring questions are a reliable indicator of where your own documentation or process maturity needs refinement.\n- Procuring external advice selectively and ad-hoc rather than permanently. Instead of building a full internal compliance team early on, it is often more cost-efficient in the founding phase to work with selective external advice—for instance, for the initial regulatory classification of the business model or for reviewing central contract documents—while ongoing implementation is managed internally.\n\nThe common denominator of these building blocks: they do not require a large compliance organisation, but primarily consistency and fixed routines—qualities that become increasingly difficult to retrofit as a company grows if they are not part of the corporate culture from the start.\n\n Conclusion\n\nFor growing InsurTechs, the question is not whether compliance processes must keep pace with company growth, but how this alignment can be achieved organisationally. Practice shows that compliance in the sector is long no longer understood as a tiresome chore, but increasingly as a matter for executive management and a prerequisite for growth. Those who anchor this responsibility early and consciously in corporate management rather than professionalising it retrospectively under acute resource pressure not only avoid regulatory risks, but also gain an independent head start in trust compared to established market participants."
}
Read article
20 August 20265 min read
BIPRO
RClassic or RNext? Why specialist maturity determines the right standard generation
20 years of BiPRO – this anniversary was at the heart of BiPRO Day 2026 at the Dorint Kongresshotel Düsseldorf/Neuss. With around 500 participants, over 40 speakers, and more than 300 member companies, the association has long become the central authority for digital standards in the insurance industry. However, alongside a retrospective, and artificial intelligence, another forward-looking topic dominated the presentations: the relationship between the established standard generation RClassic and the newer generation RNext.
Read article
19 August 20264 min read
BIPRO
AI Meets BiPRO Standards: Why Structured Interfaces Are Essential for Automated Case Processing
Artificial intelligence was the dominant topic at BiPRO Day 2026 – and precisely in the anniversary year when BiPRO e.V. celebrated its 20th existence. At first glance, this may seem surprising: Why is a two-decade-old interface standard needed when modern AI systems can supposedly process unstructured data? However, the BiPRO community at the event took a clear opposing stance: Artificial intelligence does not replace standards – it makes them more important than ever. This is because powerful AI systems require structured, quality-assured, and semantically unambiguous data to function reliably.
Read article
18 August 20264 min read
BUSINESS
Why BiPRO is not an IT project but a matter for the boardroom
In many smaller brokerages and insurance companies, the question of BiPRO connectivity is still delegated to the IT department – or to the external service provider who already looks after the broker management system (MVP). That is understandable, because BiPRO sounds technical: interfaces, standards, data formats. Yet this reflex regularly leads to an expensive misconception. BiPRO is neither a law nor a finished product that you simply buy and install – it is a voluntary industry standard whose benefits only unfold through deliberate entrepreneurial decisions.
Read article
17 August 20265 min read
DEVELOPMENT
API-first in insurance: why interface architecture decides time-to-market
For a long time, APIs were regarded in the insurance industry as a purely technical detail – a means of connecting systems internally. That view has fundamentally changed. APIs are no longer merely technical tools but highly strategic corporate assets that directly influence revenue growth, innovation and market positioning. The global market for API management is estimated at more than 16 billion US dollars in 2026, with an annual growth rate of around 34 per cent (Source: Orbilontech) – an indicator of how far API architecture has evolved from an IT-internal question into a business topic in its own right.
Read article
16 August 20265 min read
SECURITY
Certified, but secure? What ISO 27001 & TISAX truly mean for insurance IT service providers
Any IT service provider operating in the insurance sector can hardly avoid security certifications. Tenders demand them, clients set them as a contractual prerequisite, and board members often refer to them as proof of "audited security". However, in practice, there is often confusion about which certificate is actually relevant for which purpose – and what a certificate can achieve, but also what it cannot. In particular, the confusion between ISO 27001 and TISAX regularly leads to misunderstandings in the insurance industry.
Read article
13 August 20265 min read
SECURITY
DORA in Practice: What Insurers and IT Service Providers Really Need to Consider in 2026
Since 17 January 2025, the Digital Operational Resilience Act (DORA) has applied directly in all EU member states. For banks, insurance companies, payment service providers, and other financial undertakings, this marked the end of a multi-year preparation phase. However, in 2026, the nature of the regulation has noticeably changed: pure documentation obligation has become active supervision. BaFin has unequivocally declared 2026 a test of endurance – the focus is no longer on whether DORA has been implemented, but how stringently.
Read article
10 August 20265 min read
DEVELOPMENT
Legacy Systems in Core Insurance: Modernise, Replace or Encapsulate?
Insurance companies were among the pioneers of digital data processing – and that is precisely what is increasingly becoming a burden. The industry's early adoption of technology means that many core insurance systems have grown organically over decades instead of being fundamentally modernised. The result: highly complex, hard-to-maintain system landscapes that no longer meet today's requirements for flexibility, speed and external collaboration. Even seemingly simple adjustments can cause enormous effort, because data is held redundantly and has to be maintained in many places at once.
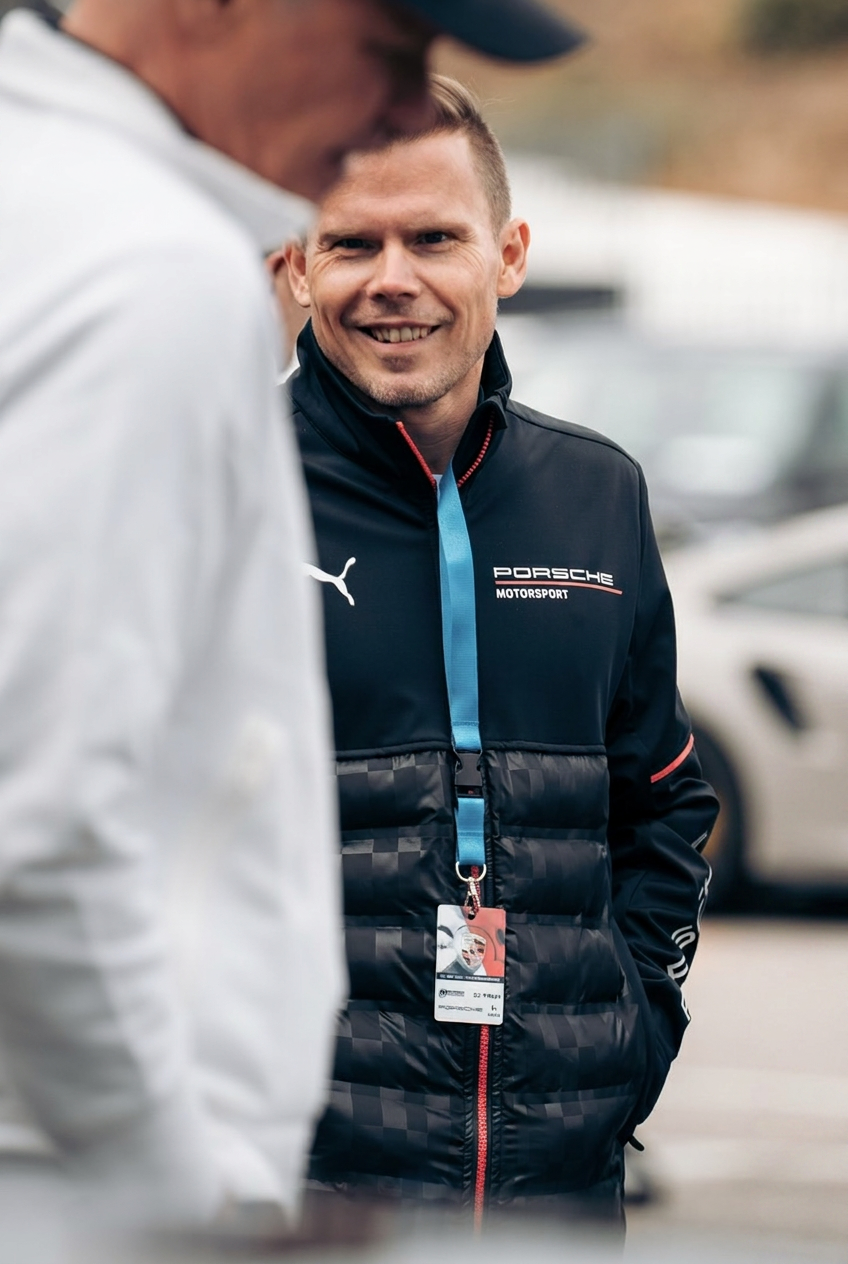
Beyond his professional life, his fascination belongs to motorsport. Out of a small circle of Porsche enthusiasts, he formed a privately organised racing team — cars from several decades of Porsche GT history, driven where they belong: on the race track.
The team from Pforzheim is independent, privately financed and opens its garage to young talents without a factory background. Racing lived honestly and without compromise — and proof that enthusiasm turns into execution.
 blau direkt Gruppe